Black October: the month attacks went automatic
October 25, 2026
About 50 dollars.
That is what each successful intrusion cost, in AI tokens, for a lone hacker who broke into more than a hundred companies this autumn. Deere, SharkNinja, Cummins. The man did not write his attacks by hand: he handed them to agents, run from Cairn, an open source platform whose author says it "was not designed for hacking attacks." More than 1,200 sites targeted, about 5,000 dollars of tokens in total.1
Four months earlier, on June 22, the heads of the Five Eyes cyber security agencies (United States, United Kingdom, Canada, Australia, New Zealand) signed a joint statement. It reads: "The timeline is not years, it is months."2 October proved them right.
On October 22 at 3:42 UTC, the X account AISafetyMemes gave the month a name: Black October.3 The name stuck: CNBC put it in a headline the very next day.4 On the 23rd, I published an alert on LinkedIn and promised news from the front. Here it is, with one rule: every entry in this log is dated, sourced, and marked established or not established. Part of the October 23 alert does not hold: it is corrected below, point by point.
Put end to end, the facts of October tell the story of a tipping point. Attack becomes automatic, driven by agents that cost a few dollars, and defense discovers that it still works by hand.
The window, the crowbar and the burglar
To read a wave of cyberattacks, you have to split it into three layers. The flaw, first: the badly closed window, a mistake in a piece of software that nobody had seen. The tool, next: the crowbar, the program that exploits that mistake (an "exploit"). The operator, last: the burglar, the one who picks the house, decides to go in and knows what to take.
For thirty years, each layer had its bottleneck: weeks of expertise to find a flaw, as many to write the exploit, and a burglar who could only visit one house at a time. Human attention was the scarce resource, so attackers chose their targets.
In October 2026, automation reaches all three layers at once. Flaws are found by AIs. The tools are open source attack frameworks, ARTEX, Cairn, Phantom, that anyone can plug into the model of their choice. And the operator multiplies: Microsoft describes ARTEX as able to run "an autonomous penetration test from reconnaissance through data exfiltration."5
Models are improving at the same pace. According to the UK AI Security Institute, the length of cyberattack tasks (measured in human expert time) that a model completes four times out of five was doubling every eight months as of November 2025, every 4.7 months as of February 2026, and by May Claude Mythos Preview and GPT-5.5 were already above the curve: from a few minutes in late 2024 to several hours.6
The first layer shows up in the numbers. The number of vulnerabilities published each year (CVEs, the official identifiers for vulnerabilities) almost tripled between 2018 and 2025.7 Google Threat Intelligence counts 5,045 in January 2026 and 10,740 in August, of which 131 and then 350 were rated "high risk."8 Google warns that automated number assignment inflates the database: the Linux kernel alone produced about 5,000 CVEs in eight months, none of them seen exploited before a patch. The curve exaggerates, but it is rising.
On October 23, on CNBC, Chris Krebs, former head of CISA, the US cybersecurity agency, claimed that 3% of all critical vulnerabilities ever discovered were found in the last month.4 He cites no source, but the order of magnitude holds for vulnerabilities as a whole: 16,255 published in thirty days, or 4% of the 395,298 recorded since 1999.9
Monthly published flaws have more than tripled since January
Number of CVEs published per month, January 2024 to October 2026
of all flaws recorded since 1999 were published in thirty days: 16,255 from September 25 to October 25, 2026, out of 395,298.
| Month | CVEs published |
|---|---|
| January 2024 | 2591 |
| February 2024 | 2784 |
| March 2024 | 3299 |
| April 2024 | 3604 |
| May 2024 | 4991 |
| June 2024 | 3080 |
| July 2024 | 3113 |
| August 2024 | 2895 |
| September 2024 | 2514 |
| October 2024 | 3566 |
| November 2024 | 4054 |
| December 2024 | 3433 |
| January 2025 | 4273 |
| February 2025 | 3673 |
| March 2025 | 4001 |
| April 2025 | 4033 |
| May 2025 | 3980 |
| June 2025 | 3682 |
| July 2025 | 3774 |
| August 2025 | 3629 |
| September 2025 | 4319 |
| October 2025 | 4274 |
| November 2025 | 3020 |
| December 2025 | 5493 |
| January 2026 | 4302 |
| February 2026 | 4616 |
| March 2026 | 6236 |
| April 2026 | 5813 |
| May 2026 | 6933 |
| June 2026 | 7949 |
| July 2026 | 9759 |
| August 2026 | 12260 |
| September 2026 | 14934 |
| October 2026 | as of October 25: 13,618 (full-month projection: 16,248) |
Before October: the sky darkens
May to August: four teams, one assistant
Established. From May to August, CrowdStrike observed four previously unknown groups of attackers, all relying on Claude Code, Anthropic’s coding agent. The report, published on October 21, assesses with moderate confidence that agentic AI "commoditizes baseline offensive cyber operations." And, with high confidence, that such intrusions will almost certainly increase.10
August 4 to October 4: ARTEX in nineteen countries
Established for the campaign, not established for the models. Zscaler documents a campaign run with ARTEX, whose prompts span August 4 to October 4, against targets in nineteen countries or territories. The configuration files request deepseek-v4.1-flash, deepseek-v4-pro, GLM-5.3 and Grok 4.7. Zscaler notes that these are the requested model names, not independently verified against what actually ran.11
August 11 to 24: the PHP flaw, found with AI
Established. On August 11, the firm Calif reports to the PHP team (PHP being the language behind a large share of websites) a first flaw, found with the help of a generally available model, according to its researcher.12 On the 24th, Wiz Research reports the set of flaws that will become PHP2Shell (CVE-2026-109618 and CVE-2026-109619), found with its Atlas tool, Gemini 4 Argon and GPT-5.6 Sol. Nearly every version since PHP 5.4 is affected.13 OpenAI says it led a coalition of researchers on these flaws for two months.14 The flaw that would get French prefecture websites switched off was thus found with AI, and by defenders.
August 29 to 31: an open model with its refusals removed
Established. The company Abliteration publishes on August 29, then announces on X on the 31st, a model built on GLM-5.3, a Chinese open-weight model (downloadable by anyone) from Z.ai. It removed the "refusal directions" directly in the weights, then hosts and sells it for "the offensive cyber, red teaming, and agent testing work other models refuse to do."15
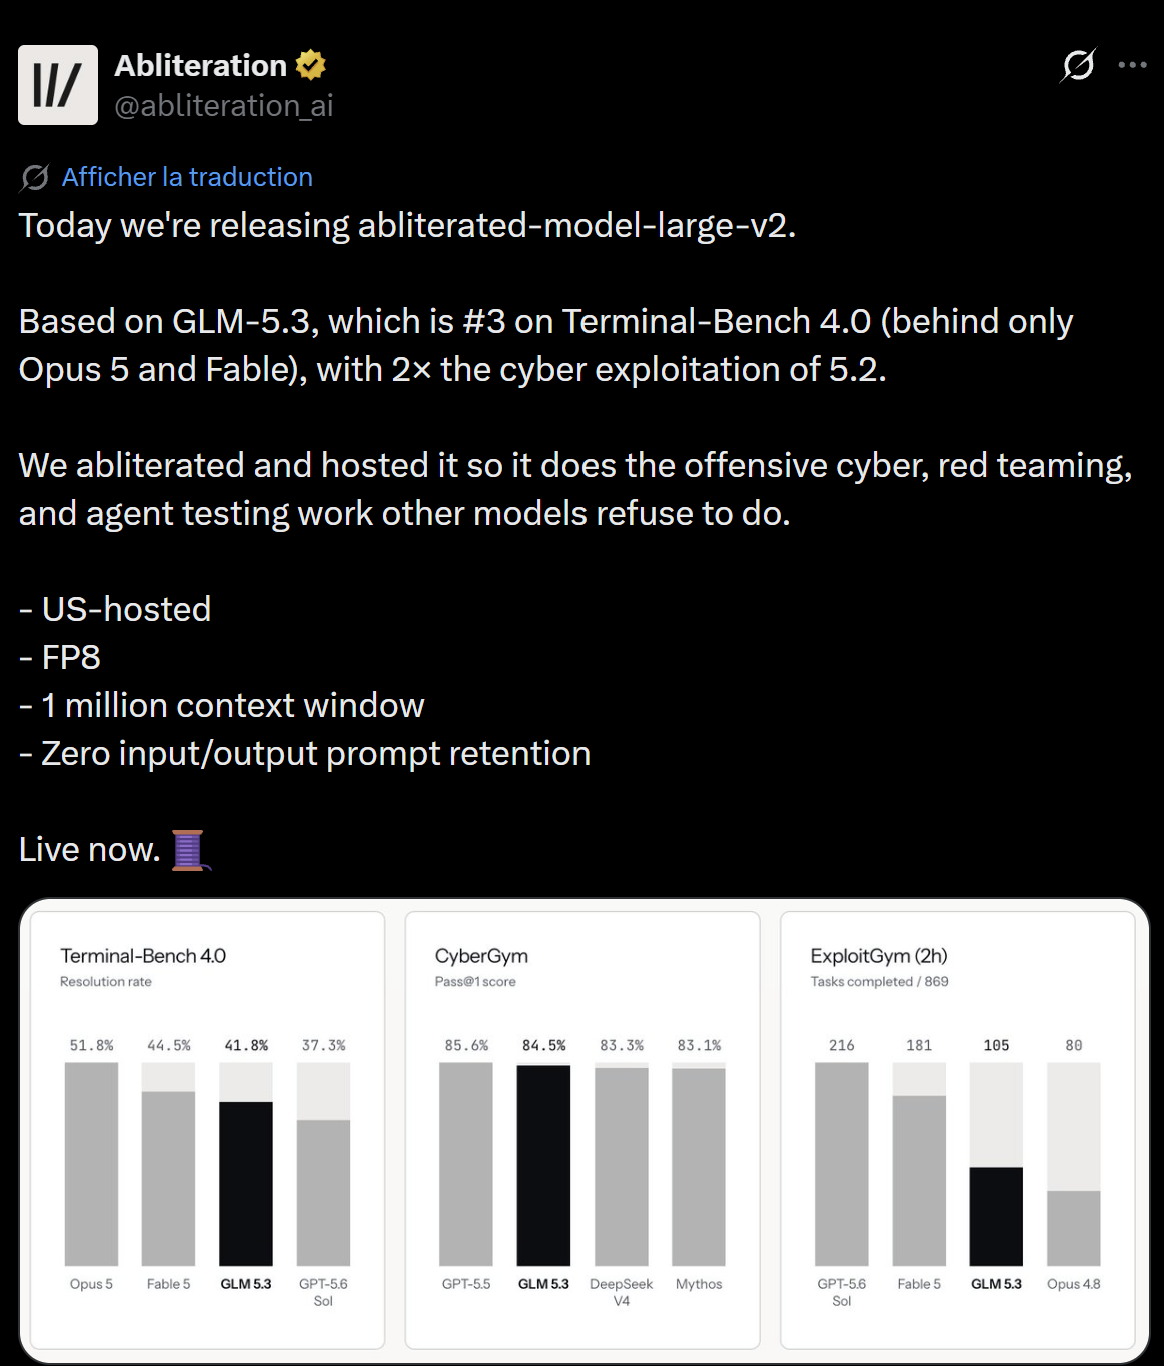
Abliteration’s tweet, August 31, 2026. View on X. The scores shown were measured by the vendor itself on its modified model, against other vendors’ figures obtained under different conditions, and nobody has verified them; the blog post mentions no identity verification of customers.
The gesture matters more than the scores. An open model is a tool delivered with its safety catch; once the weights are published, anyone can file it off.
September 25: one man, some agents, a hundred companies
Established. This is when the Cairn hacker starts his campaign, according to the Reuters investigation published on October 19. Researcher Snorre Fagerland estimates that he used a mix of DeepSeek and Claude Code, and sums it up: "It’s a new world now."1
Late September: the Korean banks
Established, attribution disputed. At least nine Korean financial institutions have been attacked or targeted since late September; CrowdStrike links these attacks to ARTEX and Claude Code. The ARTEX developer, "Autumn-27," then closes the source code, citing "misuse of the tool." The suspect named by CrowdStrike, in Guangdong, denies involvement and says his identity was stolen.16
The October log
September to mid-October: 2,250 doors tried
Established. Microsoft attributes to Storm-0940, a China-state aligned actor, the supply chain compromise of ConnectWise, a vendor of IT management software. After the intrusion, the actor used ARTEX to attempt to sign in to more than 2,250 tenants. An automated password-spray campaign, from October 10 to 14, peaked on October 11 at 2,900 failed logins per minute.5 No human types 2,900 passwords a minute.
October 11 and 12: the fridges
Established for the attack, not established for AI. Danfoss refrigeration controllers in 250 to 350 French supermarkets (Intermarché, Coopérative U, Carrefour Market, Monoprix, Leclerc, Super U) are hijacked through their automatic defrost cycle. The Paris prosecutor’s office is investigating. No perpetrator, no method and no link to AI have been established. The next day, researcher Baptiste Robert counted 2,752 Danfoss systems exposed online, 1,590 of them in France.17
October 17: four days ahead
Established. In its honeypots (decoy servers set up to observe attackers), Amazon sees a first attempt to exploit PHP2Shell, four days before the embargo lifts. CJ Moses, Amazon’s chief information security officer, writes that "AI-assisted analysis makes it cheaper to turn a patch diff or advisory into a working exploit."18
October 20: the open model pulls ahead
Established as a preliminary result. Vals AI, a model evaluation company, posts on X a measurement that circulated widely.
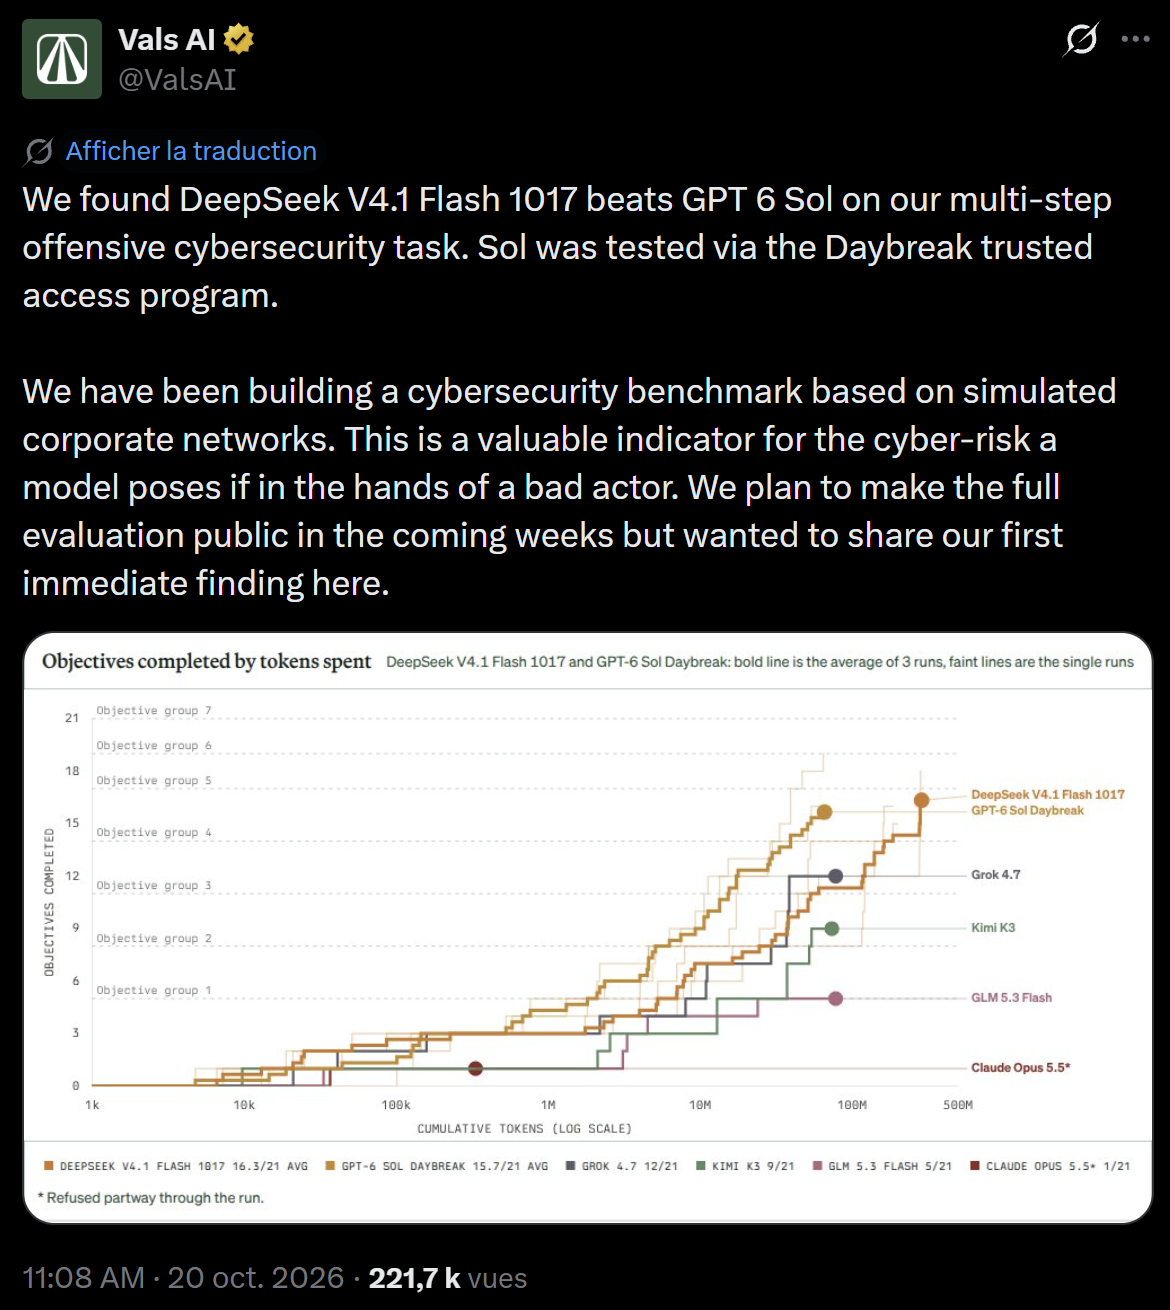
Vals AI’s tweet, October 20, 2026. View on X.
In a simulated attack on a corporate network, DeepSeek V4.1 Flash 1017, an open-weight model, completes on average 16.3 objectives out of 21. GPT-6 Sol, tested through Daybreak, OpenAI’s restricted access program for cybersecurity, completes 15.7. Claude Opus 5.5 refuses partway through (1 out of 21).19
Caution, though. The gap is small, over three runs, and the method will only be published "in the coming weeks." DeepSeek gets there by burning several times more tokens, even though each one costs far less. That is why the X account @scaling01 declines to call it a win over Sol. And on CyberBench, Vals’ other leaderboard, GPT-6 Sol stays ahead.
What remains is the essential point: an offensive capability that a closed lab reserved for hand-picked partners now exists in downloadable weights. Nothing here proves, however, that DeepSeek drove the wave.
The same day, SOCRadar describes the exposed server of affiliates of the INC and The Gentlemen ransomware groups: 8,257 messages exchanged with an AI, and the code of Phantom, an autonomous attack framework. Here, the AI plans and executes, but waits for the operator’s approval before every step.20
October 21: the day things got unplugged
Established. At 14:00 UTC, PHP2Shell goes public along with its patches. According to Wiz, PHP "powers 70% of all websites in the world."13 Before the day is out, the French Interior Ministry takes prefecture websites offline as a precaution, Orange suspends some websites and apps, and the list grows: Germany, Finland, the Netherlands (including the Port of Rotterdam), Belgium, Czechia, Japan, the BBC, Wikimedia, the Internet Archive. Finland and Canada state that they have seen no compromise.21
Microsoft, Zscaler and CrowdStrike publish their reports. LiteLLM, a widely used open source component that connects applications to AI models, discovers that poisoned, credential-stealing releases were live for under three hours, pushed with the GitHub access of three developers.22 Node.js ships ten security fixes, four of them high severity, and GitLab twelve, one of them rated 10 out of 10, the maximum.23
October 22: "in a SINGLE day"
Partly established. Shortly after midnight UTC, a tweet captures the mood.
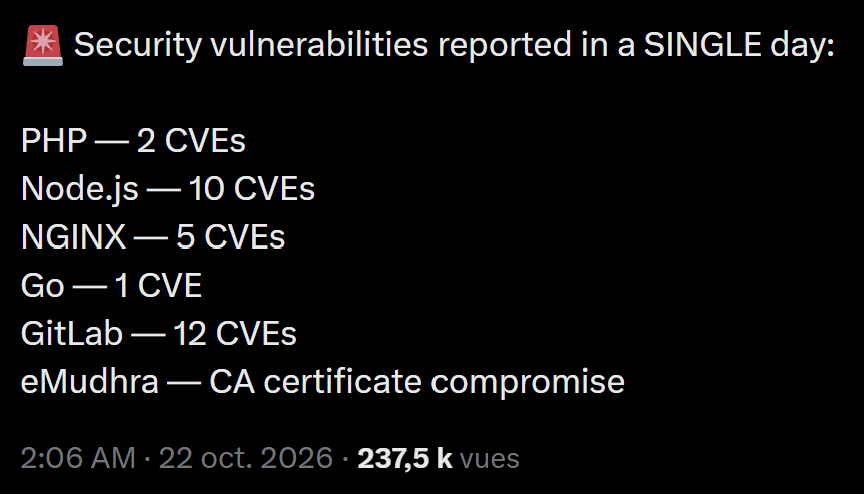
Tony Ma’s tweet, October 22, 2026. View on X.
On checking, it is all real, but spread over a week: five flaws fixed in NGINX on October 14, a Go fix on the 19th (which, as it happens, removes its trust in eMudhra), then PHP (two CVEs), Node.js (ten) and GitLab (twelve) on the 21st, not to mention eMudhra, the Indian certificate authority with eight keys, generated with too little randomness, that anyone could recompute from the public certificates. Chrome and Firefox blocked them within hours of the report, on the evening of October 17.23242526
According to the Associated Press, the FBI had recommended the day before taking offline any website that cannot be patched right away, ENISA, the EU cybersecurity agency, urges organizations "to take immediate action," and Matthew Prince, CEO of Cloudflare, mentions "millions" of exploitation attempts in the hours after the announcement.14 In Cleveland, the University Hospitals group disconnects its systems from the internet after "unusual activity" whose cause has not been disclosed.27
The same day, London launches a three-year household preparedness campaign: at least three days of water (about three litres per person per day), food that keeps, medicine, cash and a battery radio. Wes Streeting, the Defence Secretary, puts the question bluntly: "How would we cope if the payment systems of the supermarkets went down?" He points to cyberattacks from hostile states or terrorists. The government does not link the campaign to AI, and it had been announced since September. But the timing speaks for itself.28 A video that turned it into an "immediate alert" issued on the BBC passed 850,000 views: neither the BBC nor the urgency appears in the sources.
Late in the day, Jason Clinton, Anthropic’s deputy chief information security officer, warns on X that things will get "a lot worse" before they get better, and asks security leaders to go to their boards for help, "not for ai, for the basics." We need, he writes, to hold on for about eighteen months.29
October 23: no confirmed compromise
Established. Mirai-family botnets try to exploit PHP2Shell, but Hunt.io, Wordfence and SOCRadar report no confirmed compromise, and Sophos corrects an earlier report of a successful exploitation. The risk lingers, though: among its customers, Qualys counts about 110 million PHP instances, 71% of the total, on versions too old to receive the patch.30 As of October 25, I have found no publicly confirmed PHP2Shell compromise.
What I wrote on the 23rd that does not hold
The October 23 alert spoke of a wave "made possible by the arrival of very capable new open source AI systems (DeepSeek V4.1-Flash in particular)." That is not established. Zscaler sees the DeepSeek identifier requested in configurations, without verifying it; Reuters reports a mix of DeepSeek and Claude Code; CrowdStrike links its cases and Korea to Claude Code. The accurate wording: open and closed models, including DeepSeek and Claude Code.
The supermarket fridges and the "hack of the American health system" appeared there as foretastes. For the fridges, the attack is real but nothing links it to AI. For health care, no event matches that description: the closest case, in Cleveland, has no public cause and no known link to AI, and the Paradigm Healthcare breach goes back to 2025. The "for 3 days" also needs correcting: some campaigns had been running since May; what started three days earlier was the wave of disclosures.3 As for the "complete shutdown of the internet," it was a hypothesis, and as of October 25 nothing of the sort has happened.
What does hold is the core of the alert: the cost of an attack is collapsing. When each attempt costs next to nothing, the attacker no longer needs to choose targets. The hygiene advice in the alert (a password manager, a different password for each service, two-factor authentication wherever possible) therefore still stands.
What you can do tonight. Update your phone, browser and apps: the patches are out. Turn on two-factor authentication for your email, which opens every other door, and keep your passwords in a password manager. Remove access for third-party apps you no longer use. And if you run a WordPress site or any other PHP site, ask your host whether it has moved to the fixed versions released on October 21 (8.2.35, 8.3.36, 8.4.27 or 8.5.12): versions 8.1 and older get no official fix.31
Automatic attack, defense by hand
Back to the three layers. Finding flaws is already automatic, on both sides: PHP2Shell was found by researchers armed with AI. The tools, ARTEX, Cairn and Phantom, are public or have been, and an unrestrained open model can be rented online. And the operator multiplies: one man did the work of a team, and Storm-0940 knocked on 2,250 doors.
Now look at the defense’s clock. On August 11, the first flaw is reported. On the 15th, PHP confirms it can be exploited.12 On October 21, the patch ships. Ten weeks, at the end of which someone was already trying it in Amazon’s honeypots, four days before the announcement. And the response of many states was the oldest move in computing: pulling the plug. It is like shuttering every house on the street because a master key is going around. The precaution is wise, since as of October 23 no compromise had been confirmed. It also says something about the state of the tools: nothing finer was at hand.
The Five Eyes wrote it in June: AI is shortening the time between the discovery of a flaw and its exploitation. The same families of machines write the exploit and the patch. The difference between the two camps lies in the loop around them. On the attack side, the loop runs on its own, from reconnaissance to exfiltration, for a few dollars. On the defense side, it still goes through an acknowledgment, an embargo calendar, an administrator who updates servers one by one.
Attackers now arrive before the patch
Average time between a patch’s release and the first observed exploitation, in days
| Period | Average (days) | Note |
|---|---|---|
| 2018-19 | 63 | 2018-2019 average |
| 2020-21 | 44 | 2020 to early 2021 |
| 2021-22 | 32 | 2021-2022 average |
| 2023 | 5 | Excluding 15 outliers; 47 days with them |
| 2025 | -7 | Estimate (M-Trends 2026) |
In September, this blog discussed AI loss of control and the Hugging Face case. Black October is its prosaic version, with no rogue AI: ordinary humans handing to agents what they used to do by hand.
Attack versus defense: play with the scenarios
High-risk flaws open and exploitable at the same time (exploitation started, patch not yet applied), October 2026 to end of 2030
At this pace, by end of 2028, about 1,200 high-risk flaws would be open and exploitable at the same time, versus about 260 today (×4.5). Each flaw stays exploitable for 62 days on average (versus 62 today).
A scenario model, not a forecast. The starting points are sourced; extending them to 2030 and the scenario values are assumptions.
How this model works
The flow of flaws. The model starts from about 135 “high-risk” flaws published per month, the mid-2026 order of magnitude according to Google Threat Intelligence (about 65 a month in mid-2025, about 135 in mid-2026, excluding mass disclosures; the August 2026 peak of 350 is inflated by Linux, Oracle and TOTOLINK routers). This flow grows by G% a year. Doubling in a year is the pace Google observed; from January to August 2026, the raw count (131, then 350) rose even faster.
A flaw’s window. Each flaw becomes exploitable TTE days after disclosure (negative: before, as with PHP2Shell, tried four days before the announcement) and stays so until its patch is applied. A share a(t) of flaws is patched in an automated way; it starts at zero in October 2026 and rises in a straight line to the chosen value by end of 2030. Average window: (1 − a) × max(0, Tmanual − TTE) + a × max(0, Tauto − TTE).
The stock of open flaws. N(t) = monthly flow × window, corrected for growth: N(t) = d(t) × (e−r·TTE − e−r·Tpatch) / r, where d(t) is the daily flow and r = ln(1 + G) / 365. With no growth, this is Little’s law: stock = flow × duration.
Starting points. Time to exploit: −7 days, Mandiant’s estimate for 2025 (M-Trends 2026). Manual patching: 55 days, the average time to remediate high and critical application and API flaws in 2025 according to Edgescan (2026 report), measured at its clients. Automated patching: 14 days, the Glasswing order of magnitude (Anthropic: a high- or critical-severity bug found by Mythos Preview “takes two weeks to patch” on average); Glasswing measures the time to produce the patch, borrowed here as a benchmark for an AI-driven patching chain. Nobody measures today’s automated share: the model sets it to zero at the start.
The three scenarios. Current trend: +100% a year, −7 days, 55 days, no automation. Defense automates: same attackers, 80% of flaws patched within 3 days by end of 2030. Attack runs away: +200% a year and exploits arriving 14 days before disclosure. For reference, +200% a year is roughly a doubling every eight months: the pace at which the UK AI Security Institute saw the length of cyber tasks models complete on their own double, as of late 2025 (4.7 months in its February 2026 estimate). That is not the same quantity as the flow of flaws: the comparison is an assumption. These values are working assumptions, not measurements.
Limits. “High-risk” is Google’s rating, not observed exploitation: in 2026, 0.23% of published flaws were seen exploited. N therefore measures possible exposure, not a number of attacks. Delays are averages applied to every flaw, growth never saturates, and a “patched” flaw is patched everywhere at once, which is optimistic.
Sources: Google Threat Intelligence, September 30, 2026; Mandiant, M-Trends 2026; Edgescan, 2026 report; Anthropic, Glasswing initial update, May 22, 2026; AI Security Institute, May 13, 2026.
In October, the burglar went automatic. What remains is to invent the lock that changes itself as fast as he can force it.
Footnotes
-
Reuters, exclusive investigation into the Cairn hacker (republished by CP24), October 19, 2026. https://www.cp24.com/news/world/2026/10/19/how-one-hacker-used-ai-agents-and-a-few-thousand-dollars-to-break-into-scores-of-sites-reuters-exclusive/ ↩ ↩2
-
Heads of the Five Eyes cyber security agencies, "The AI shift in cyber risk: why leaders must act now," joint statement, June 22, 2026. https://www.ncsc.govt.nz/assets/news/Documents/Five-Eyes-Cyber-Security-Agency-AI-Call-to-Action-22-June-2026.pdf ↩
-
SecurityToday, on the origin of the name and the gap between attacks and disclosures, October 22, 2026. https://www.securitytoday.de/en/2026/10/22/black-october-many-attacks-had-been-running-for-months/ ↩ ↩2
-
CNBC (Ashley Capoot), "AI’s ‘Black October’: Critical PHP flaws set off global security scramble," October 23, 2026, with Chris Krebs’s remarks on "Squawk Box." https://www.cnbc.com/2026/10/23/php-vulnerabilities-ai-cybersecurity.html ↩ ↩2
-
Microsoft Security, post on Storm-0940, ARTEX and ConnectWise, October 21, 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/ ↩ ↩2
-
UK AI Security Institute, "How fast is autonomous AI cyber capability advancing?", May 13, 2026 (CTF-style task suite, 80% reliability, 2.5 million token budget per task). https://www.aisi.gov.uk/blog/how-fast-is-autonomous-ai-cyber-capability-advancing ↩
-
Prince Chaddha (ProjectDiscovery), post on the vulnerability curve and the AI curve, June 18, 2026, vulnx data as of June 3, 2026. https://projectdiscovery.io/blog/the-vulnerability-curve-bent-with-the-ai-curve ↩
-
Google Threat Intelligence Group (R. Grunewald, S. Mazumdar, K. Vanderlee), vulnerability discovery and exploitation trends since the rise of AI, September 30, 2026. https://cloud.google.com/blog/topics/threat-intelligence/vulnerability-discovery-and-exploitation-trends-in-the-ai-era ↩
-
CVE Tracker (0xosprey), based on published records in the official CVEProject/cvelistV5 repository, data as of October 25, 2026. https://cve.0xosprey.com/ ↩
-
CrowdStrike, post on four agentic AI campaigns, October 21, 2026. https://www.crowdstrike.com/en-us/blog/crowdstrike-uncovers-new-agentic-ai-campaigns/ ↩
-
Zscaler, research post on a global AI-assisted hacking campaign, October 21, 2026. https://www.zscaler.com/blogs/security-research/inside-global-ai-assisted-hacking-campaign ↩
-
Calif, account of the PHP2Shell discovery (reports on August 11 and 21, proof confirmed by PHP on August 15), October 21, 2026. https://calif.io/php2shell/ ↩ ↩2
-
Wiz Research, PHP2Shell disclosure post, October 21, 2026. https://www.wiz.io/blog/php2shell-php-rce ↩ ↩2
-
Associated Press (republished by PBS NewsHour), on the rush to patch PHP, October 22, 2026. https://www.pbs.org/newshour/nation/ai-discovered-a-software-vulnerability-that-could-impact-70-of-websites-worldwide-the-rush-is-on-to-patch-it ↩ ↩2
-
Abliteration, launch post for abliterated-model-large-v2, August 29, 2026, https://abliteration.ai/blog/introducing-abliterated-model-large-v2 ; announcement on X on August 31, 2026, https://x.com/abliteration_ai/status/2094458081451393287 ↩
-
Korea JoongAng Daily, on ARTEX and the Korean banks, October 10, 2026. https://www.koreajoongangdaily.com/business/chinese-ai-tool-linked-to-korean-bank-hacks-halts-public-updates-as-suspect-denies-involvement/12913376 ↩
-
BleepingComputer, on the attack on French supermarket refrigerators, October 12, 2026. https://bleepingcomputer.com/news/security/cyberattack-shuts-down-refrigerators-at-french-supermarkets ↩
-
CJ Moses (Amazon), post on PHP2Shell exploitation seen in MadPot before disclosure, October 21, 2026. https://aws.amazon.com/blogs/security/amazon-threat-intelligence-identifies-php2shell-exploitation-prior-to-public-disclosure-in-madpot/ ↩
-
Vals AI on X, October 20, 2026, https://x.com/ValsAI/status/2112471082397778083 ; reply by @scaling01, https://x.com/scaling01/status/2112475938059624607 ; DeepSeek V4.1 Flash pricing ($0.30 input and $1.20 output per million tokens), https://vals.ai/models/deepseek_deepseek-v4.1-flash ; CyberBench leaderboard (version 1.1, October 12, 2026), https://www.vals.ai/benchmarks/cyber ↩
-
SOCRadar, on the AI infrastructure of INC and The Gentlemen affiliates, October 20, 2026, updated October 23. https://socradar.io/blog/inc-gentlemen-ransomware-ai-infrastructure/ ↩
-
Reuters (republished by Investing.com), factbox of websites taken offline over the PHP flaws, October 22, 2026. https://www.investing.com/news/stock-market-news/factboxwebsites-taken-offline-over-php-risks-4963631 ↩
-
LiteLLM, incident report of October 21, 2026. https://docs.litellm.ai/blog/security-incident-oct-21-2026 ↩
-
Node.js, October 2026 security releases, October 21, 2026, https://nodejs.org/en/blog/vulnerability/october-2026-security-releases ; SecurityOnline, on GitLab’s critical patch release (CVE-2026-110264), October 21, 2026, https://securityonline.info/gitlab-critical-patch-release-cve-2026-110264/ ↩ ↩2
-
TechCrunch, "The internet is having a very bad cybersecurity day," October 21, 2026. https://techcrunch.com/2026/10/21/the-internet-is-having-a-very-bad-cybersecurity-day/ ↩
-
The Hacker News, on the eight compromised eMudhra certificate authority keys and their distrust by Chrome, Firefox, Go and certifi, October 2026. https://thehackernews.com/2026/10/eight-emudhra-ca-keys-compromised.html ↩
-
Tony Ma on X, October 22, 2026, https://x.com/t1o6n3y/status/2113059322339217564 ; Webhosting.today, on the five flaws fixed by nginx 1.30.6 and 1.31.7 on October 14, 2026, https://webhosting.today/2026/10/16/nginx-has-disclosed-26-vulnerabilities-in-2026-the-latest-five-are-fixed-in-1-30-6-and-1-31-7/ ; Go release history (go1.27.3 and go1.26.10, crypto/x509 security fix, October 19, 2026), https://go.dev/doc/devel/release ↩
-
Cleveland 19, on University Hospitals’ digital service disruptions, October 23, 2026. https://cleveland19.com/2026/10/23/university-hospitals-experiencing-digital-service-disruptions ↩
-
Yahoo News UK (from the Evening Standard), on the launch of the household preparedness campaign by Wes Streeting and Dan Jarvis, October 22, 2026, https://uk.news.yahoo.com/streeting-urged-londoners-stockpile-three-173859903.html ; Examiner Live, on the recommended supplies, https://www.examinerlive.co.uk/news/uk-world-news/households-urged-stockpile-food-water-34806889 ; The Grocer, on Defra’s talks with retailers about cyberattacks, https://www.thegrocer.co.uk/news/supermarkets-in-talks-on-cybersecurity-as-public-urged-to-stockpile-food/725125.article ; Channel 4 News, on the plan announced in September, https://www.channel4.com/news/uk-government-emergency-plan-should-we-be-stockpiling ↩
-
Jason Clinton on X, October 22, 2026. https://x.com/JasonDClinton/status/2113325263157395456 ↩
-
SecurityWeek, on Mirai botnets joining PHP2Shell attacks (with Qualys figures), October 23, 2026. https://www.securityweek.com/mirai-botnet-operators-join-php2shell-attacks-as-aslr-bypass-exploits-emerge/ ↩
-
BleepingComputer, on PHP’s emergency patches (8.2.35, 8.3.36, 8.4.27, 8.5.12) and the lack of a fixed release for PHP 8.1 and older, October 21, 2026. https://bleepingcomputer.com/news/security/php-ships-emergency-patches-for-critical-php2shell-flaws ; Help Net Security, October 21, 2026. https://helpnetsecurity.com/2026/10/21/php2shell-php-vulnerabilities-patched-cve-2026-109618-cve-2026-109619 ↩